 Fedigest
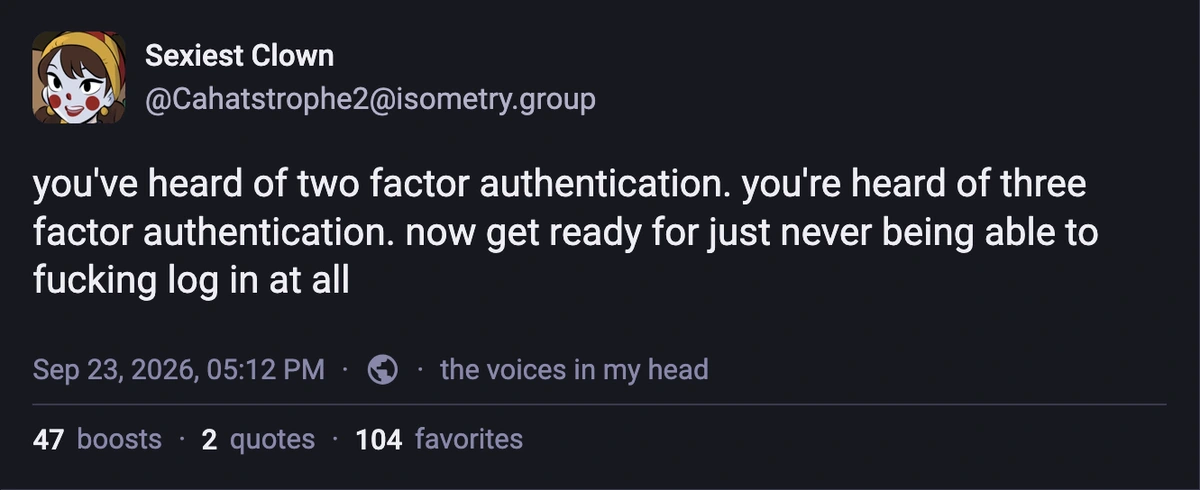
Source: https://mstdn.isometry.group/@Cahatstrophe2/117323121764942610
::: spoiler transcript @Cahatstrophe2@isometry.group: you've heard of two factor authentication. you're heard of three factor authentication. now get ready for just never being able to fucking log in at all :::
I miss my old 486 with DOS and Windows 3. No login, no updates, no subscriptions and collaboration only with actual physical friends coming over. New software from the computer market or pirated by sharing floppy discs on the schoolyard...
I'm nostalgic about my 486,but I don't miss it. I had the 25 Mhz, MEGAHERTZ not GHz version and it was pretty damn slow. The upgrade to the 100Mhz chip was great but it wasn't until multicore CPUs before I felt that computers got fast enough for me.
I mean get Linux and don't update?
Doesn't give me the nostalgia feeling and is also multi user by design.
You won't get back that LAN only world of the past but in Linux and even Windows you can simply disable network adapters/controllers. Maybe if I ever have kids I'll recreate a LAN only environment for them.
Sites keep pushing Passkeys on me. I tried them. Did not work cross device. Did not integrate with every app. For now, I gave up on them.
It’s only a secure technology when it works and the key turns in the lock.
works cross-device with third party password managers (or smart keys like yubikeys)
Which defeats the point doesn't it
Common misconception. The whole point of a password manager is so that you can have a unique password for every account. This means that of one site is compromised, only that one site is lost.
Passkeys take this a step further by taking a keylogger out of the equation since you’re no longer typing the password. And by using biometrics instead of a password to unlock your password manager, no password is ever typed significantly reducing the ability to steal it. Even better if it asks for both.
And to the point of one point of failure, this is always the case as you could get knocked on the head and forget all your passwords. You now only have to manage one potential point of security failure rather than however many accounts you have online.
Yeah I don't like those things. If your password is two or three words, with a special character and 3 numbers anywhere before between or after, it would take millions of years to brute force, and then you're still covered with auth codes 2 factor. Theres no point in having a password so complex that you yourself can't remember it.
The only exception is when a common password is found in a data breach, but you should have unique passwords for work and financial accounts and theres no guarantee that the password managers won't be hacked at some point.
That's what Google use. I lost access to a Google account even though I had the right password because they randomly decided they didn't think I was the account owner, and I didn't have a phone number attached so the account recovery wasn't available
Same thing happened with my Binance account. Then when I finally started to get some traction with customer service, my state banned Binance. And now it's effectively gone forever
I kept seeing a popup about adding a phone number because I might lose access to my account. I removed the phone number a decade ago. You mean my recovery email, OTP code, and backup codes can't be used for recovery motherfucker!?!
Anyway I exported everything and closed my account because the fascists can eat a dick.
They may work, this was years ago before OTP was so widespread, and I don't remember if it had a recovery email associated or not. I just remember I had the right password and it wouldn't let me in anyway
meanwhile there are LLM call centers with no authentication
I called one, and the only authentication they asked was my birthday. instead of asking me my name or other details it just said "please confirm, are you [full name]?"
that's all the security to access my private data!
then after going nowhere I managed to be transferred to a human and it took them a few minutes to authetify me.
Me after setting up SSH on a server and unable to log in remotely:
Time to go back to communication via letter and telephone and read encyclopedias.
I've been there, deleted my Gmail a while back and then two weeks later realized it was attached to a login I didn't want to lose.
most sites when you use a vpn
Oh, we already have that last option at work. Has made work soo much nicer.